




Ports need to prepare for cyber attacks
Being prepared is key to ports ensuring resilience against the ‘inevitability’ of a cybersecurity attack.
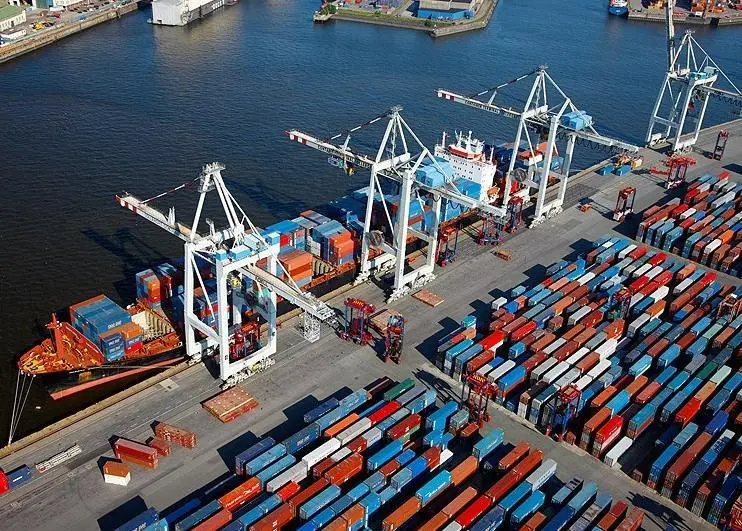
That was the key message when experts from the maritime and security industries met at the IAPH World Ports Conference webinar to discuss how to foster resilience against the ‘digital tempest’ ports face.
Challenges from threat actors include QR fishing, malware and driver exploitation. And with it taking an average of a month for organisations to fully recover from a loss of service, ports need to ensure that they can operate without their systems for 30 days.
“Ports are the gateway to global trade, the pulse point of economies,” said Jens Meier, chief executive of Hamburg Ports Authority and president of IAPH.
“By implementing these strategies and staying vigilant about emerging threats we are not just protecting our individual ports, we are safeguarding our entire global maritime trade network.”
Two-fold approach
Being prepared is critical with a two-fold approach of both resilience and crisis management key to minimising disruption. Organisations must be able to both respond to an attack and minimise its likelihood, emphasised Ram Levi, founder and chief executive of cybersecurity firm, Konfidas.
Each party knowing their own responsibilities is key in responding quickly and effectively, not only at management level but throughout the port, he said.
“What will be the response plan of customs, what will be the plan of the gate in and gate out, who’s going to speak to the media, who’s going to speak to the employees?” said Levi.
“Everybody needs to have a concise plan.”
Levi pointed to four key strategies – proactive planning and risk assessment, robust business continuity plans, an effective incident response and regular training and simulations – to ensure that ports can respond quickly and effectively.
Know your role
The need for this preparedness was echoed by Tony Zhong, chief information security officer at the Port of Los Angeles, who said that policies and procedures need to be in place.
“During an attack is not the time to figure out whose responsibility a service is,” he said. “Is it the vendor’s or is it the internal team’s? Take the time to work that out beforehand.”
Key processes include service level agreements with suppliers and understanding procurement to ensure that the port has the right solutions in place.
“In the digital age cybersecurity is not just an IT issue, it’s a fundamental aspect of port management,” said Meier.
“Just as we wouldn’t dream of running a port without physical security measures, we can’t run modern ports without robust cyber security.”
Related Articles
 DIGITAL
 PRODUCTS & SERVICES
 PRODUCTS & SERVICES