






ISPS compliance: some did, some didnt
The press releases came in from every corner of the world. Those ports and shipowners that had complied wanted to shout about it. Fair enough considering the effort and expense involved in preparing for ISPS Code compliance by the 1 July deadline – but too many to list here individually.
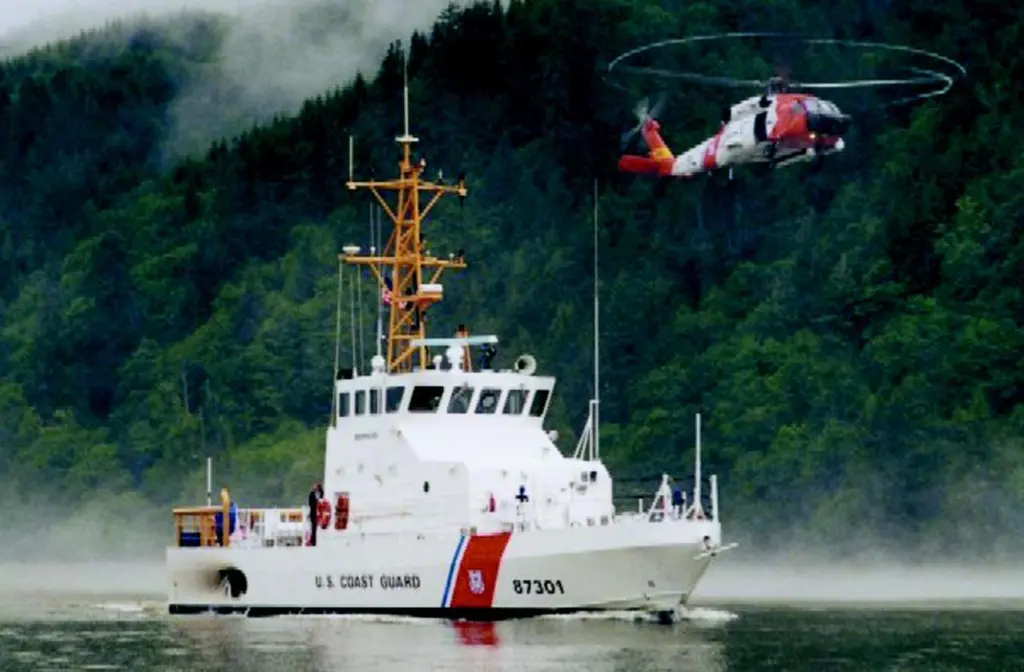
A week after the introduction of the International Ship and Port Facility Security Code, Lloyd’s List reported that the US Coast Guard had carried out 442 security examinations on vessels bound for US ports, 428 of which were pier-side and 14 at sea, identifying 49 ships that were not in compliance with the Code. Of those non-compliant vessels, nine were denied entry to port, 10 were expelled from port and 30 more were detained or forced to restrict their operations.
Meanwhile a survey amongst European Sea Ports Organisation (ESPO) members during the last week of June showed that all main European port facilities met the deadline set by the Code and the EU Regulation on ship and port facility security.
In many countries ports managed to have all or nearly all port facility security plans approved on time. In other countries plans of the most important port facilities handling the biggest share of traffic were approved on time.
Remaining port facility security plans were “expected to be approved shortly. In some countries plans are substantially operational but final implementation measures may take another two to three months, ” says ESPO.
The survey anticipates that compliant ships will not in most cases be able to visit a non-compliant port and this will lead to ships being diverted.
But significantly, the survey also demonstrated that ESPO members are still faced with a number of unresolved concerns, namely:
the handling of ships which are not certified or have been handled at non-certified port facilities during one of their previous calls distortion of competition between ports on the implementation of the ISPS code including concerns about the readiness of ports outside the EU and inspections on implementation by IMO, EU and other instances coordination between authorities and port facility security officers when security breaches occur and overall coordination between port and government agencies costs and financing compatibility and competition with land transport modes and nodal points which as yet do not have an overall security system similar to the ISPS code or EU regulation.
Elsewhere, on 1 July Singapore reported that all 80 vessels which called since the code came into force were compliant.
Not all ports were well prepared themselves but the various consultants which have sprung up in response to the Code’s demands are helping out. Working with funds from the US Agency for International Development and the private sector, the Caribbean Basin Maritime Security Alliance contracted with SeaSecure to perform a security compliance survey of all the international ports in over nine countries. The Alliance is headed by Caribbean-Central American Action, an independent organisation that promotes private sector-led economic development in the Caribbean Basin.In a report commissioned by the Florida Ports Council, SeaSecure stated that, as of June the majority of ports in the Caribbean region had yet to meet all the requirements set forth in the ISPS Code.
Some of the reasons cited include a lack of effective communications between governments and the ports;
insufficient capital to institute costly security infrastructure improvements;
and, a paucity of maritime security expertise and experience.However, in the event ports were unable to carry out the recommendations called for in their security assessments, the Code provides some relief.
The port may institute an ‘alternative’ programme wherein some temporary measure that provides equivalent risk mitigation is used in the interim.
Alternative plans will be used by many Caribbean ports to become compliant while they secure funding or installation of assessment-recommended risk mitigation measures.
Related Articles
 EQUIPMENT
 EQUIPMENT